Phishing Attacks Evolve: Identifying the Newest 2026 Tactics and Protecting Your Digital Assets
Anúncios
Phishing Attacks Evolve: Identifying the Newest 2026 Tactics and Protecting Your Digital Assets
In the relentless landscape of cyber warfare, one threat consistently adapts and reinvents itself: phishing. What began as simple email scams has morphed into a sophisticated, multi-faceted assault on individuals and organizations alike. As we navigate 2026, understanding the latest evolutions in phishing attack evolution is not just prudent; it’s absolutely critical for safeguarding our digital assets. The adversaries are no longer just sending misspelled emails; they are employing artificial intelligence, exploiting complex supply chains, and leveraging psychological manipulation with unprecedented precision.
Anúncios
This comprehensive guide delves into the cutting-edge tactics employed by cybercriminals in 2026. We will explore how AI is being weaponized, the rising danger of supply chain phishing, the psychological nuances of social engineering, and the critical importance of a layered defense strategy. Our goal is to equip you with the knowledge and tools necessary to identify these advanced threats and fortify your digital perimeter against the ever-present danger of phishing attack evolution.
The Shifting Sands of Phishing: A Historical Perspective
To truly grasp the current state of phishing attack evolution, it’s essential to briefly look back. The term ‘phishing’ itself emerged in the mid-1990s, primarily associated with AOL accounts where attackers ‘fished’ for passwords. These early attempts were rudimentary, often relying on poor grammar and obvious inconsistencies. However, their effectiveness lay in the novelty of the internet and a general lack of user awareness.
Anúncios
The 2000s saw a rise in mass-market phishing campaigns, often targeting financial institutions. These emails would impersonate banks, urging recipients to ‘verify’ their account details on fake websites. The focus was on quantity over quality, hoping a small percentage of recipients would fall victim. As anti-spam filters improved and user awareness grew, attackers began to refine their methods.
The 2010s introduced spear phishing, a highly targeted attack where criminals research their victims to create personalized and convincing emails. Whaling attacks, targeting high-profile executives, also gained prominence. This era marked a significant shift towards quality and personalization, making detection far more challenging. Mobile phishing (smishing) and voice phishing (vishing) also emerged as smartphones became ubiquitous.
By the early 2020s, ransomware often accompanied phishing, and business email compromise (BEC) schemes became incredibly lucrative. The rise of sophisticated fake login pages, often indistinguishable from legitimate ones, further blurred the lines. And now, in 2026, we face an even more complex and insidious array of threats, driven by technological advancements and increasingly organized criminal enterprises. Understanding this trajectory is key to appreciating the current challenges in combating phishing attack evolution.
AI-Powered Phishing: The New Frontier of Deception
The advent of advanced Artificial Intelligence (AI) has revolutionized many industries, but it has also provided cybercriminals with potent new weapons for phishing attack evolution. In 2026, AI is no longer just a tool for detection; it’s a formidable engine for deception. The following are some of the most concerning AI-driven phishing tactics:
Deepfake Technology in Vishing and Smishing
Perhaps the most alarming development is the use of deepfake technology. AI-powered voice synthesis and video manipulation has reached a level of sophistication where it’s incredibly difficult for the human ear or eye to discern fakes from reality. Imagine receiving a call from what sounds exactly like your CEO, urgently requesting a wire transfer, or a video conference call where a deepfake of a trusted colleague asks you to click a malicious link. These scenarios are no longer theoretical. Attackers can now:
- Mimic Voices with Precision: AI can analyze short audio clips of a target’s voice and generate new speech with astonishing accuracy, replicating tone, cadence, and even emotional inflections. This makes vishing attacks incredibly convincing.
- Create Realistic Video Impersonations: Deepfake video technology can create convincing visual representations of individuals, used in fake video calls or recorded messages. This is particularly dangerous for high-stakes business communications.
The implications for corporate espionage, financial fraud, and personal identity theft are profound. Verifying identities in a deepfake world requires more than just listening or watching; it demands robust authentication protocols.
AI-Generated Spear Phishing Content
Gone are the days of poorly written phishing emails. AI, particularly large language models (LLMs), can now generate highly personalized, grammatically perfect, and contextually relevant spear phishing emails at scale. These AI tools can:
- Craft Flawless Language: Overcoming language barriers and grammatical errors that were once tell-tale signs of phishing.
- Personalize Content Extensively: By scraping public data from social media, professional networks, and corporate websites, AI can tailor messages to individual victims, referencing specific projects, colleagues, or recent events to build trust and urgency.
- Optimize for Engagement: AI can even A/B test different subject lines and message bodies to maximize click-through rates, making campaigns far more effective.
The sheer volume and quality of AI-generated content make it exceedingly difficult for traditional email filters and even human vigilance to detect. This represents a significant leap in phishing attack evolution.
Behavioral Phishing with AI
Advanced AI models can analyze user behavior patterns – their typical online activities, working hours, communication styles, and even their emotional responses to certain stimuli. This allows attackers to launch ‘behavioral phishing’ attacks that are timed and designed to exploit specific vulnerabilities. For instance:
- An email might arrive during a known busy period, when the victim is more likely to be distracted.
- The tone of the message might be crafted to induce panic or curiosity, based on the victim’s known psychological profile.
This level of psychological manipulation, powered by AI, makes these attacks incredibly insidious and difficult to defend against, as they bypass many traditional security awareness training modules.
Supply Chain Phishing: A Growing and Insidious Threat
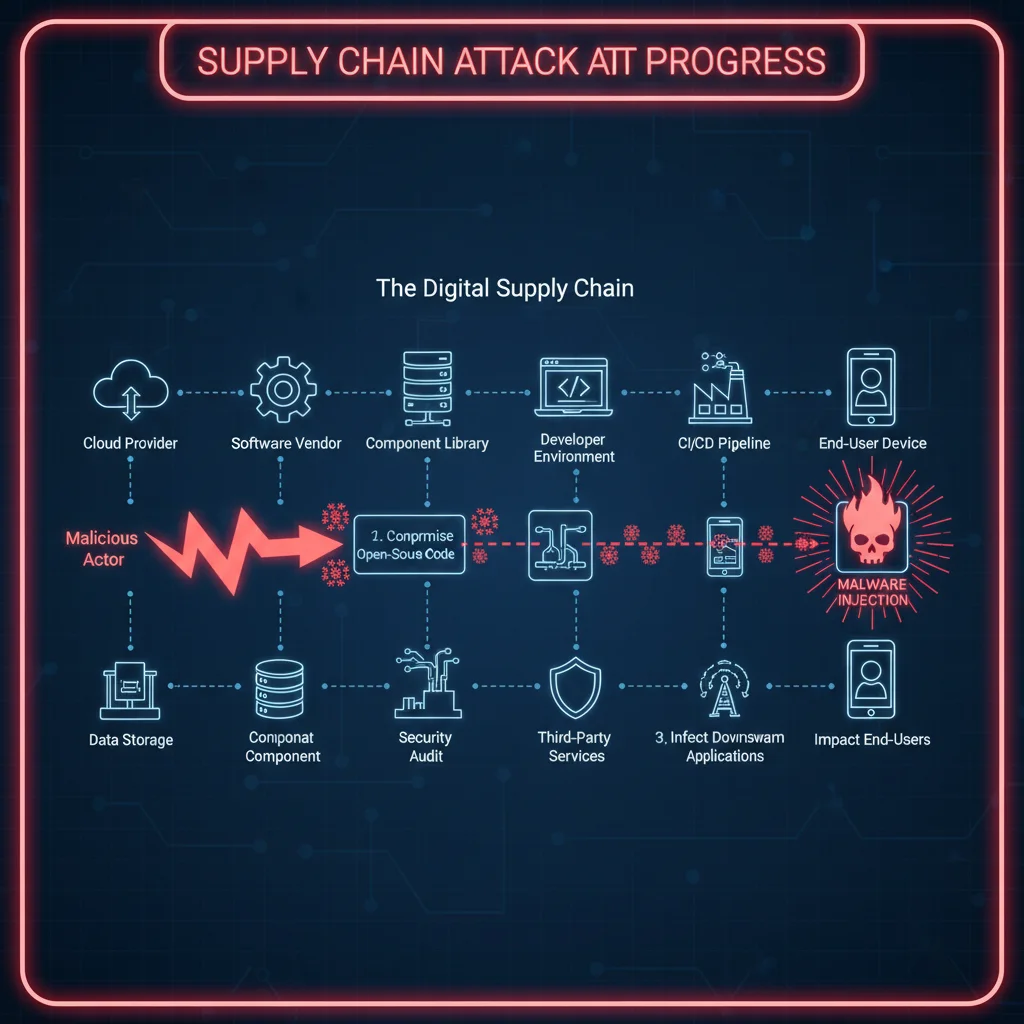
Beyond the direct assault on individuals, 2026 has seen a dramatic increase in supply chain phishing attacks. This tactic exploits the trust inherent in business relationships, targeting organizations by compromising their vendors, partners, or service providers. The goal is to leverage a trusted third party’s access or reputation to gain entry into the primary target’s systems or to deceive their employees.
Compromising Trusted Vendors
Attackers recognize that large organizations often have robust security measures. Instead of a direct frontal assault, they target smaller, less secure vendors that have legitimate access to the larger organization’s systems or data. Once a vendor’s system is compromised, attackers can:
- Distribute Malware through Trusted Channels: Inject malicious code into software updates or legitimate files provided by the compromised vendor.
- Send Phishing Emails from a Trusted Domain: Use the compromised vendor’s email system to send highly credible phishing emails to employees of the target organization. These emails appear to come from a known and trusted source, making them incredibly effective.
- Gain Access to Sensitive Data: Leverage the vendor’s access to exfiltrate data from the target organization.
The SolarWinds attack in 2020 served as a stark reminder of the devastating impact of supply chain compromises, and in 2026, these attacks have become even more sophisticated and widespread as part of phishing attack evolution.
Cloud Service Provider Exploits
Many organizations rely heavily on cloud service providers (CSPs) for infrastructure, software, and data storage. Threat actors are increasingly targeting these CSPs to launch widespread phishing campaigns. By compromising a CSP, attackers can:
- Access Multiple Client Accounts: A single breach at a CSP can expose hundreds or thousands of client organizations to phishing.
- Inject Malicious Code into Cloud Applications: Alter legitimate cloud-based applications to serve phishing pages or deliver malware.
- Leverage Cloud Identity and Access Management (IAM): Exploit weaknesses in CSP’s IAM to gain unauthorized access to client resources, then use this access to launch internal phishing campaigns.
The interconnected nature of cloud environments means that a breach in one area can have a cascading effect, making supply chain phishing through CSPs a particularly potent threat.
Third-Party Application Integration Risks
The proliferation of APIs and third-party application integrations has created new vectors for phishing. Attackers can:
- Exploit API Vulnerabilities: Find weaknesses in APIs used by third-party applications to inject malicious content or redirect users to phishing sites.
- Impersonate Integrated Services: Create convincing fake login pages for popular integrated services (e.g., CRM, project management tools, communication platforms) to steal credentials.
- Leverage OAuth Phishing: Tricking users into granting malicious applications access to their legitimate accounts through seemingly benign OAuth requests.
Organizations must conduct rigorous security assessments of all third-party integrations and ensure that their partners adhere to stringent cybersecurity standards to mitigate this aspect of phishing attack evolution.
Advanced Social Engineering Techniques: The Human Element
While technology advances, the human element remains the most vulnerable link in the security chain. In 2026, social engineering tactics have become extraordinarily sophisticated, often leveraging psychological principles to manipulate victims into divulging information or performing actions detrimental to their security. This is a critical component of phishing attack evolution.
Pretexting and Impersonation Refined
Pretexting, where an attacker creates a fabricated scenario to engage with a victim, has become an art form. Attackers invest significant time in researching their targets to build incredibly believable pretexts. This includes:
- Deep Background Research: Utilizing open-source intelligence (OSINT) from social media, corporate websites, news articles, and even dark web forums to gather intimate details about a target’s professional and personal life.
- Crafting Believable Narratives: Developing stories that resonate with the victim’s interests, responsibilities, or vulnerabilities. This could be an urgent request from a ‘superior,’ a ‘technical support’ call, or an ‘HR issue.’
- Multi-Channel Attacks: Combining email, phone calls, and even social media interactions to reinforce the fake persona and build a sense of legitimacy and trust over time.
The goal is to establish rapport and credibility, making the victim more likely to comply with requests that would otherwise raise suspicion.
Exploiting Cognitive Biases and Emotional Triggers
Cybercriminals are increasingly leveraging principles of psychology to exploit human cognitive biases and emotional triggers. These include:
- Urgency and Scarcity: Creating a false sense of immediate danger or limited opportunity to bypass rational thought processes (e.g., ‘Your account will be suspended in 5 minutes!’).
- Authority Principle: Impersonating figures of authority (CEOs, government officials, law enforcement) to induce compliance.
- Social Proof: Suggesting that ‘everyone else is doing it’ or citing endorsements from ‘trusted’ sources.
- Fear and Greed: Appealing to primal emotions by threatening negative consequences or promising lucrative rewards.
- Curiosity: Enticing users with intriguing but malicious content.
These psychological ploys are often integrated into AI-generated phishing content, making them exceptionally difficult to resist without specialized training and constant vigilance against phishing attack evolution.
Quid Pro Quo and Baiting
These techniques offer something in return for information or access:
- Quid Pro Quo: Offering a service or benefit (e.g., ‘free software update,’ ‘security audit’) in exchange for credentials or access. This often involves attackers posing as IT support.
- Baiting: Offering enticing but false promises (e.g., ‘free movie downloads,’ ‘exclusive discounts’) to trick victims into downloading malware or revealing information. Physical baiting, like leaving infected USB drives in public places, also persists.
The effectiveness of these methods lies in their ability to play on human desires and the natural inclination to accept helpful offers, even from unfamiliar sources.
Defending Against the Evolving Phishing Landscape in 2026
Combating the advanced phishing attack evolution of 2026 requires a multi-layered, proactive, and continuously updated defense strategy. No single solution is sufficient; a combination of technological safeguards, robust policies, and comprehensive human training is essential.
Technological Safeguards
Implementing and maintaining state-of-the-art security technologies forms the bedrock of your defense:
- Advanced Email Security Gateways: These systems must go beyond traditional spam filtering. They need AI-powered threat detection, sandbox analysis for suspicious attachments and links, and URL rewriting/scanning to detect malicious redirects. They should also be capable of detecting deepfake indicators in multimedia attachments.
- Multi-Factor Authentication (MFA) Everywhere: MFA, especially hardware-based FIDO2 keys, is the most critical defense against credential theft. Even if an attacker obtains a password, MFA prevents unauthorized access. Implement MFA across all critical systems, applications, and accounts.
- Endpoint Detection and Response (EDR) and Extended Detection and Response (XDR): These solutions provide continuous monitoring of endpoints and networks, detecting anomalous behavior that might indicate a successful phishing attempt or malware infection. They are crucial for rapid response and containment.
- DNS Filtering and Web Security Gateways: Blocking access to known malicious websites and categorizing potentially dangerous domains can prevent users from reaching phishing sites even if they click a malicious link.
- Zero Trust Architecture: Adopt a ‘never trust, always verify’ approach. Every user, device, and application must be authenticated and authorized, regardless of whether they are inside or outside the network perimeter. This limits the damage if a phished credential is used.
- AI-Powered Anomaly Detection: Utilize AI and machine learning to detect unusual login patterns, strange email sending behaviors, or abnormal data access attempts that could signify a phishing compromise.
- Data Loss Prevention (DLP): Implement DLP solutions to prevent sensitive information from being exfiltrated, even if an attacker gains access to internal systems.
Robust Policies and Procedures
Technology alone is not enough. Strong organizational policies and incident response plans are vital:
- Strict Access Controls and Least Privilege: Grant users only the minimum necessary access to perform their job functions. Regularly review and revoke unnecessary privileges.
- Incident Response Plan for Phishing: Develop and regularly test a clear, actionable plan for responding to suspected or confirmed phishing incidents. This includes communication protocols, containment steps, and recovery procedures.
- Regular Security Audits and Penetration Testing: Proactively identify vulnerabilities in your systems, applications, and processes before attackers can exploit them.
- Vendor Security Management: Implement a rigorous process for vetting and continuously monitoring the security posture of all third-party vendors and supply chain partners. Include security clauses in contracts and conduct regular audits.
- Email Authentication Protocols (SPF, DKIM, DMARC): Ensure these protocols are correctly configured to prevent email spoofing and verify the legitimacy of incoming emails.
Continuous Security Awareness Training
The human element is often the weakest link, but it can also be your strongest defense with proper training. This training must be ongoing and adapt to the latest phishing attack evolution:
- Interactive and Engaging Training: Move beyond annual PowerPoint presentations. Utilize gamified learning, interactive modules, and real-world scenarios to make training memorable and effective.
- Simulated Phishing Attacks: Regularly conduct realistic phishing simulations to test employee vigilance and identify areas for improvement. Provide immediate feedback and remedial training for those who fall victim.
- Deepfake Recognition Training: Educate employees on the existence and dangers of deepfake technology. Provide specific guidance on how to verify identities in voice and video communications (e.g., using pre-arranged codewords, calling back on a known number).
- Recognizing Social Engineering Tactics: Train employees to identify common psychological manipulation techniques used in phishing, such as urgency, authority, and emotional appeals.
- Reporting Mechanisms: Establish clear and easy-to-use channels for employees to report suspicious emails, calls, or messages without fear of reprimand. Encourage a culture of ‘see something, say something.’
- Focus on Supply Chain Awareness: Educate employees about the risks associated with third-party communications and the importance of verifying unexpected requests from vendors or partners.
- Regular Updates on Latest Threats: Keep employees informed about the newest phishing attack evolution and trends through newsletters, alerts, and quick training refreshers.
The Future of Phishing: What Comes Next?
As technology continues its rapid advancement, so too will the tactics of cybercriminals. The phishing attack evolution is a continuous arms race. Looking beyond 2026, we can anticipate several emerging trends:
- Quantum Phishing: While still in its infancy, the development of quantum computing could potentially break current encryption standards, leading to new forms of phishing that exploit quantum vulnerabilities.
- Brain-Computer Interface (BCI) Exploitation: As BCIs become more prevalent, attackers might seek to exploit vulnerabilities in these interfaces to directly manipulate thoughts or extract sensitive information, though this is a more distant threat.
- Hyper-Personalized AI Agents: AI agents could become so sophisticated that they can engage in long, multi-turn conversations, building trust and extracting information over extended periods, making them even harder to detect than current AI-generated content.
- Augmented Reality (AR) and Virtual Reality (VR) Phishing: As AR/VR environments become more integrated into daily life, attackers may create convincing fake virtual environments or inject malicious elements into legitimate ones to trick users.
- Swarm Phishing: The use of multiple, coordinated AI agents to launch simultaneous, diverse phishing attacks, overwhelming defenses and increasing the chances of success.
Staying ahead of these future threats requires continuous research, adaptability, and a commitment to evolving our security postures as rapidly as the threats themselves.
Conclusion
The landscape of phishing in 2026 is complex, challenging, and constantly changing. The integration of AI, the exploitation of supply chains, and the refinement of social engineering tactics have elevated phishing from a nuisance to a significant existential threat for individuals and organizations. The battle against phishing attack evolution is not one that can be won with a single solution or a one-time effort.
It demands a dynamic, multi-faceted approach encompassing cutting-edge technological safeguards, rigorously enforced policies, and, crucially, continuous, adaptive human training. By understanding the newest tactics, fostering a culture of vigilance, and implementing robust defenses, we can collectively strengthen our digital resilience and protect our invaluable digital assets from the ever-present and evolving danger of phishing. The time to act and adapt is now.