Cybersecurity Threats 2026: Protecting Your Digital Presence in the US
Anúncios
Cybersecurity Threats in 2026: Protecting Your Digital Presence in the US from 3 Common Attacks
The digital landscape is in constant flux, evolving at an unprecedented pace. As we look towards 2026, the complexity and sophistication of cybersecurity threats are projected to reach new heights, posing significant challenges for individuals, businesses, and critical infrastructure across the United States. The interconnectedness of our modern world, while offering immense benefits, also creates a vast attack surface that malicious actors are eager to exploit. Understanding these emerging cybersecurity threats 2026 is not merely an academic exercise; it is a critical necessity for maintaining digital integrity and national security.
Anúncios
In this comprehensive guide, we will delve into the anticipated cybersecurity landscape of 2026, focusing on three prevalent attack vectors that are expected to dominate the threat horizon: sophisticated ransomware attacks, advanced AI-powered cyberattacks, and pervasive supply chain vulnerabilities. We will explore the mechanisms behind these threats, their potential impact on the US, and, most importantly, actionable strategies and robust defenses to protect your digital presence. The goal is to equip you with the knowledge and tools necessary to navigate this complex environment, ensuring resilience and security in an increasingly volatile digital world.
The urgency of this discussion cannot be overstated. From personal data breaches affecting millions to critical infrastructure disruptions that can cripple entire regions, the consequences of inadequate cybersecurity are severe. As cybercriminals become more organized, resourceful, and technologically adept, our defenses must evolve commensurately. This article serves as a crucial resource for anyone seeking to understand and mitigate the evolving cybersecurity threats 2026 will present.
The Evolving Threat Landscape: What to Expect in 2026
The year 2026 promises a cybersecurity environment characterized by heightened complexity and a relentless pursuit of vulnerabilities by threat actors. Several factors contribute to this escalation, including the rapid advancement of artificial intelligence and machine learning, the proliferation of interconnected devices (IoT), and the geopolitical tensions that often spill over into cyberspace. These elements collectively create a breeding ground for novel attack methodologies and amplify the impact of existing ones.
Anúncios
One of the most significant shifts expected is the move towards more targeted and customized attacks. Gone are the days when broad, untargeted phishing campaigns were the primary concern. While they still exist, the focus is increasingly on precision strikes, often leveraging deep reconnaissance and social engineering techniques to bypass even sophisticated defenses. This requires organizations and individuals to move beyond generic security measures and adopt a more adaptive, threat-informed defense posture.
Furthermore, the convergence of operational technology (OT) and information technology (IT) networks continues to expand the attack surface for critical infrastructure. Attacks on these systems can have devastating real-world consequences, impacting essential services like energy, water, and transportation. The US government and private sector are keenly aware of these risks, but the sheer scale and interdependence of these systems make securing them a monumental task. Understanding these overarching trends is crucial for contextualizing the specific cybersecurity threats 2026 will bring.
The Rise of Cybercrime-as-a-Service (CaaS)
A disturbing trend that will continue to mature by 2026 is the professionalization of cybercrime through Cybercrime-as-a-Service (CaaS) models. This phenomenon lowers the barrier to entry for aspiring cybercriminals, providing them with access to sophisticated tools, infrastructure, and even technical support for a fee. This means that even individuals or groups with limited technical expertise can launch devastating attacks, further increasing the volume and variety of threats.
CaaS offerings include everything from ransomware kits and phishing templates to distributed denial-of-service (DDoS) services and access to compromised networks. This commoditization of cyber warfare tools makes the threat landscape more democratic, in a perverse sense, empowering a wider range of actors to engage in malicious activities. The implications for defending against cybersecurity threats 2026 are profound, as it necessitates a defense strategy that can contend with a larger, more diverse, and less predictable adversary pool.
Organizations must recognize that they are not just fighting highly skilled state-sponsored groups, but also a growing legion of opportunistic attackers leveraging readily available tools. This demands a multi-layered security approach, emphasizing not only technical controls but also robust security awareness training for all employees, as human error remains a primary entry point for many CaaS-enabled attacks.
Threat 1: Sophisticated Ransomware Attacks
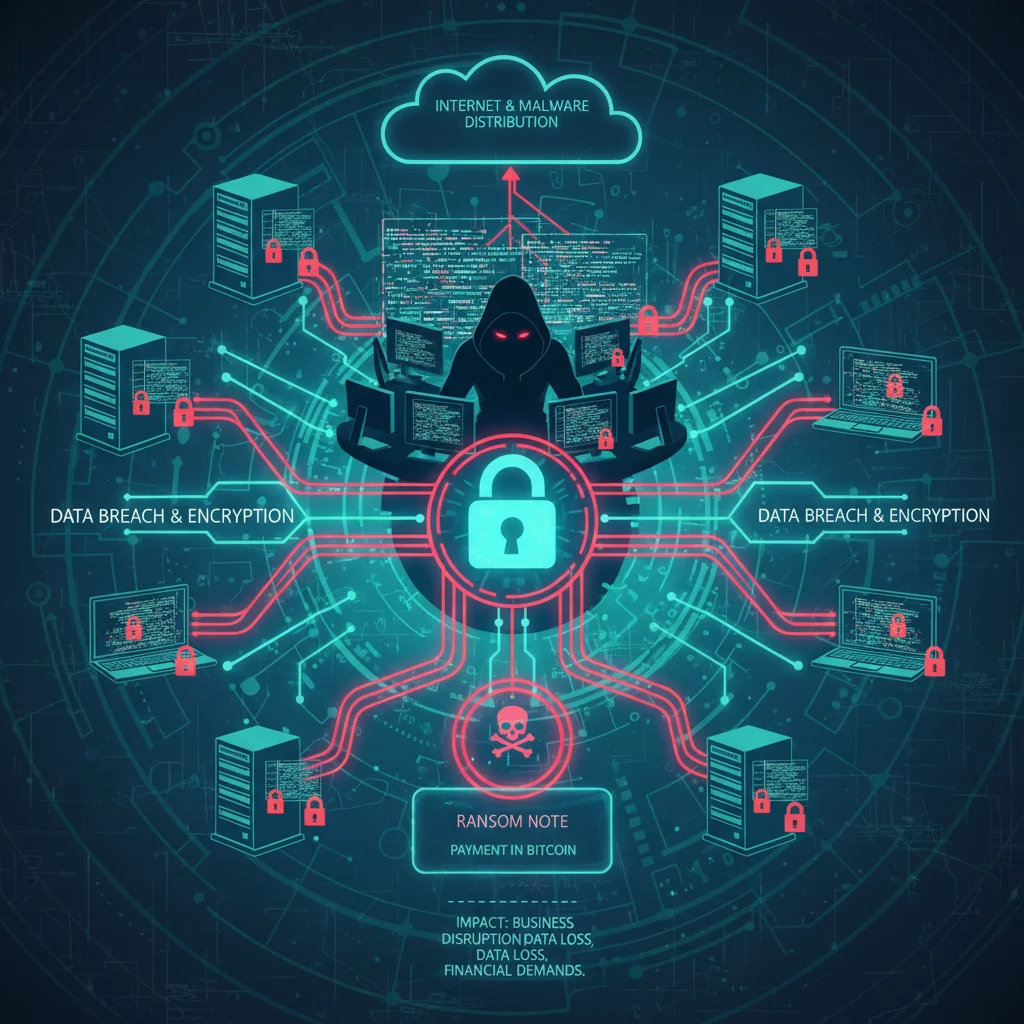
Ransomware has been a persistent and evolving threat for years, but by 2026, its sophistication is expected to reach unprecedented levels. These attacks are no longer just about encrypting files and demanding a ransom; they are becoming multi-faceted extortion campaigns designed to maximize damage and financial gain. The evolution of ransomware represents one of the most pressing cybersecurity threats 2026 will face.
Double and Triple Extortion Tactics
By 2026, ‘double extortion’ will be the standard, where attackers not only encrypt data but also exfiltrate it, threatening to publish sensitive information if the ransom is not paid. This adds immense pressure on victims, as paying the ransom does not guarantee the data will not be leaked, and non-payment can lead to severe reputational damage, regulatory fines, and competitive disadvantage.
Furthermore, ‘triple extortion’ is gaining traction, where attackers also target the victim’s customers, partners, or suppliers, threatening to disrupt their operations or publish their data if the ransom is not met. This creates a ripple effect, transforming a single breach into a widespread crisis that can impact an entire ecosystem. The complexity of these extortion models makes incident response significantly more challenging and costly.
The financial impact of these attacks is staggering, with recovery costs often far exceeding the initial ransom demand due to business disruption, reputational damage, and legal fees. For US businesses, particularly small and medium-sized enterprises (SMEs) that may lack robust security infrastructure, these attacks can be existential. Proactive measures against these advanced ransomware campaigns are paramount to mitigating the cybersecurity threats 2026 presents.
Targeting Critical Infrastructure and Supply Chains
Ransomware groups are increasingly targeting critical infrastructure organizations, recognizing the high stakes involved and the increased likelihood of a payout. Attacks on hospitals, energy grids, and transportation systems can have catastrophic consequences, disrupting essential services like energy, water, and transportation. The US government has identified this as a top national security concern, and efforts are underway to bolster defenses in these sectors.
Moreover, ransomware groups are exploiting vulnerabilities within supply chains, understanding that compromising one vendor can provide access to numerous larger, more lucrative targets. A successful attack on a software provider, for instance, can lead to widespread infections among its customer base, as seen in past high-profile incidents. This interconnectedness makes the entire digital ecosystem vulnerable to a single point of failure.
Protecting against these sophisticated ransomware attacks requires a multi-layered approach, including robust backups, strong endpoint detection and response (EDR) solutions, network segmentation, and comprehensive incident response plans. Regular security audits and employee training on identifying phishing attempts are also crucial. These measures are essential for countering the evolving cybersecurity threats 2026 poses.
Defending Against Advanced Ransomware
Effective defense against sophisticated ransomware in 2026 will demand a proactive and resilient strategy. Organizations must prioritize immutable backups, ensuring that critical data is regularly backed up to isolated, air-gapped systems that cannot be accessed or encrypted by attackers. This is the last line of defense when all other measures fail.
Beyond backups, a strong security posture involves implementing advanced threat intelligence to stay ahead of new ransomware variants. This includes subscribing to threat feeds, participating in information-sharing groups, and leveraging AI-driven security tools that can detect anomalous behavior indicative of a ransomware attack in its early stages. Endpoint protection platforms (EPP) with behavioral analysis capabilities are becoming indispensable.
Furthermore, network segmentation is vital. By dividing the network into smaller, isolated segments, organizations can contain the spread of ransomware, preventing it from compromising the entire infrastructure. Implementing a ‘zero-trust’ security model, where no user or device is trusted by default, regardless of whether they are inside or outside the network perimeter, is also a critical paradigm shift for 2026 and beyond. This comprehensive approach is essential to combat the growing cybersecurity threats 2026 will bring.
Threat 2: Advanced AI-Powered Cyberattacks
The rapid advancements in artificial intelligence (AI) and machine learning (ML) are a double-edged sword. While these technologies offer immense potential for enhancing cybersecurity defenses, they also provide powerful new tools for malicious actors. By 2026, AI-powered cyberattacks are expected to become more prevalent and sophisticated, posing a formidable challenge to traditional security measures. These represent some of the most intelligent cybersecurity threats 2026 will unleash.
AI-Enhanced Phishing and Social Engineering
AI is already being used to create highly convincing phishing emails and social engineering schemes. By 2026, generative AI models will enable attackers to craft hyper-personalized and contextually relevant messages at scale, making them virtually indistinguishable from legitimate communications. This includes deepfake voice and video technology, which can be used to impersonate executives or trusted individuals, tricking employees into revealing sensitive information or transferring funds.
These AI-enhanced attacks will be able to adapt in real-time, learning from user interactions to refine their tactics and increase their success rate. Traditional security awareness training, while still important, may struggle to keep pace with the evolving realism of these AI-generated deceptions. The human element will remain the weakest link, but AI will make exploiting that link far more effective.
The implications for corporate espionage, financial fraud, and data theft are immense. Organizations will need to invest in advanced AI-driven detection systems that can identify subtle anomalies in communication patterns and content that human eyes might miss. This proactive defense is critical against the AI-powered cybersecurity threats 2026 will introduce.
Automated Vulnerability Exploitation and Malware Generation
AI can also be leveraged to automate the process of discovering and exploiting vulnerabilities in software and systems. AI-powered tools can rapidly scan vast networks, identify weaknesses, and even develop custom exploits tailored to specific targets, all with minimal human intervention. This significantly reduces the time between vulnerability disclosure and exploitation, making it harder for defenders to patch systems in time.
Furthermore, AI can be used to generate highly polymorphic malware that can constantly change its code and behavior, making it extremely difficult for traditional signature-based antivirus solutions to detect. These ‘living’ malware strains can adapt to evade detection, learn from defensive countermeasures, and persist on compromised systems for extended periods, making them incredibly potent cybersecurity threats 2026 will have to contend with.
The arms race between AI for offense and AI for defense will intensify. Security teams will need to deploy their own AI and ML tools to analyze vast amounts of security data, detect subtle patterns of attack, and automate incident response. This includes leveraging AI for threat hunting, anomaly detection, and predictive analytics to anticipate and neutralize threats before they can cause significant damage.
Countering AI-Powered Attacks
To effectively counter AI-powered cyberattacks, a multi-pronged strategy is required. Firstly, organizations must invest in AI-driven security solutions that can analyze vast datasets, identify sophisticated attack patterns, and automate responses. This includes next-generation firewalls, intrusion detection/prevention systems (IDPS), and Security Information and Event Management (SIEM) platforms that incorporate AI/ML capabilities.
Secondly, continuous security training that includes exposure to AI-generated deepfakes and advanced phishing simulations is crucial for employees. Developing a critical eye for digital communications and verifying requests through out-of-band channels will become more important than ever. Companies should foster a culture of skepticism regarding unusual digital requests.
Lastly, robust patch management and vulnerability scanning programs are essential. By reducing the number of exploitable vulnerabilities, organizations can limit the opportunities for AI-powered attack tools to gain a foothold. Embracing a DevSecOps approach, integrating security into every stage of the software development lifecycle, will also be critical in building more resilient systems against the cybersecurity threats 2026 will bring.
Threat 3: Pervasive Supply Chain Vulnerabilities
The interconnected nature of modern business means that organizations rarely operate in isolation. They rely on a complex web of suppliers, vendors, and third-party service providers, forming an intricate global supply chain. While this interconnectedness drives efficiency and innovation, it also introduces significant cybersecurity risks. By 2026, supply chain vulnerabilities are expected to be a primary vector for major cyberattacks, representing a critical element of the cybersecurity threats 2026 landscape.
Exploiting Trust Relationships
Attackers increasingly target weaker links in the supply chain to gain access to larger, more secure organizations. A small, less-resourced vendor might become the entry point for a breach that ultimately impacts a major corporation or government agency. This strategy exploits the inherent trust relationships within the supply chain, where organizations often grant extensive access to their systems and data to their partners.
Software supply chain attacks, where malicious code is injected into legitimate software updates or libraries, are particularly insidious. These attacks can go undetected for long periods, spreading malware to thousands or millions of users who trust the integrity of their software providers. The impact of such attacks can be widespread and devastating, compromising data, intellectual property, and operational continuity.
The challenge lies in the sheer number of third parties involved and the difficulty in vetting the security practices of each one. Organizations often lack visibility into the security posture of their entire supply chain, creating blind spots that attackers are eager to exploit. Addressing these pervasive vulnerabilities is a key component of managing the cybersecurity threats 2026 will present.
Hardware and Firmware Compromises
Beyond software, hardware and firmware supply chains also present significant risks. Malicious actors can tamper with hardware components or inject backdoors into firmware during the manufacturing or distribution process. These compromises can be extremely difficult to detect, as they often bypass software-level security controls and can persist even after system reinstallation.
The globalized nature of hardware manufacturing means that components often pass through numerous hands and jurisdictions before reaching the end-user. This creates ample opportunities for state-sponsored actors or sophisticated criminal groups to introduce vulnerabilities at various stages. Detecting such sophisticated compromises requires specialized expertise and advanced hardware-level security tools, which are often beyond the reach of many organizations.
The integrity of the entire technology stack, from the silicon up, is becoming a paramount concern. Governments and large corporations are increasingly scrutinizing their hardware supply chains, but the challenge for the broader market remains substantial. This layer of vulnerability adds another complex dimension to the cybersecurity threats 2026 landscape.
Mitigating Supply Chain Risks
To mitigate pervasive supply chain vulnerabilities, organizations must adopt a holistic and continuous risk management approach. This begins with thorough vendor risk assessments, evaluating the security posture of all third-party partners before establishing relationships and on an ongoing basis. This includes reviewing their security policies, certifications, incident response plans, and conducting regular audits.
Implementing strong contractual agreements that mandate specific security requirements and audit rights for vendors is also crucial. Organizations should also consider adopting third-party risk management (TPRM) platforms that automate the assessment and monitoring of vendor security. Establishing clear communication channels for security incidents with all supply chain partners is also vital for rapid response.
Furthermore, organizations should implement stringent access controls for third-party vendors, adhering to the principle of least privilege. Network segmentation and micro-segmentation can help isolate vendor access, limiting the potential damage if a vendor’s system is compromised. For software, utilizing software bill of materials (SBOMs) can provide transparency into components and their potential vulnerabilities, enabling better risk assessment. These proactive measures are indispensable for addressing the cybersecurity threats 2026 will bring through the supply chain.
Proactive Strategies for Digital Protection in the US
Given the evolving nature of cybersecurity threats 2026, a proactive and adaptive defense strategy is no longer optional but essential. Organizations and individuals in the US must move beyond reactive measures and embrace a security-first mindset that permeates every aspect of their digital existence. This involves a combination of technological solutions, robust policies, and continuous education.
Embrace a Zero-Trust Architecture
The traditional perimeter-based security model is increasingly ineffective against modern threats. A zero-trust architecture (ZTA) assumes that no user, device, or application, whether inside or outside the network, should be trusted by default. Every access request is verified based on multiple factors, including user identity, device health, location, and the sensitivity of the resource being accessed.
Implementing ZTA involves strong identity and access management (IAM) solutions, multi-factor authentication (MFA) everywhere, micro-segmentation of networks, and continuous monitoring of user and device behavior. This approach significantly reduces the attack surface and limits the lateral movement of attackers even if they manage to breach an initial defense. For mitigating the cybersecurity threats 2026 will pose, zero-trust is a foundational principle.
Invest in Advanced Threat Intelligence and Analytics
Staying ahead of sophisticated threats requires access to timely and actionable threat intelligence. Organizations should invest in platforms that aggregate data from various sources, including industry-specific feeds, government advisories, and dark web monitoring. This intelligence can help identify emerging attack vectors, attacker methodologies, and indicators of compromise (IOCs) before an attack materializes.
Coupled with advanced analytics, AI-driven SIEM and Security Orchestration, Automation, and Response (SOAR) platforms can process vast amounts of security data, detect subtle anomalies, and automate responses to known threats. This reduces the burden on human security analysts and enables faster, more consistent incident response, which is crucial against the rapid pace of cybersecurity threats 2026.
Strengthen Human Firewalls with Continuous Training
Despite technological advancements, the human element remains the most common entry point for cyberattacks. Phishing, social engineering, and insider threats continue to be highly effective. Therefore, continuous and engaging security awareness training for all employees is paramount. This training should go beyond basic phishing tests and include simulations of advanced social engineering tactics, deepfake awareness, and incident reporting procedures.
Fostering a culture of security where employees feel empowered to question suspicious requests and report potential threats without fear of reprisal is essential. Regular drills and updated training modules that reflect the latest threat landscape will help employees become the strongest line of defense against the cybersecurity threats 2026 presents.
Robust Incident Response and Recovery Planning
Even with the most robust defenses, breaches can occur. Therefore, a well-defined and regularly tested incident response plan is critical. This plan should outline clear roles and responsibilities, communication protocols, containment strategies, and recovery procedures. It should also include provisions for legal counsel, public relations, and engagement with law enforcement.
Regular simulations and tabletop exercises can help identify gaps in the plan and ensure that teams are prepared to respond effectively under pressure. A swift and coordinated response can significantly minimize the damage and recovery costs associated with a cyberattack. Investing in cyber insurance can also provide financial protection and access to expert incident response services, offering another layer of resilience against the inevitable cybersecurity threats 2026 will bring.
The Role of Government and Collaboration
Protecting the digital presence of the US against the complex cybersecurity threats 2026 requires more than just individual organizational efforts; it demands a concerted, collaborative approach involving government agencies, private industry, and international partners. The scale and nature of these threats transcend traditional boundaries, necessitating a unified front.
Government Initiatives and Regulations
The US government is increasingly recognizing the severity of cyber threats and is implementing various initiatives and regulations to bolster national cybersecurity. This includes increased funding for cybersecurity research and development, the establishment of agencies like CISA (Cybersecurity and Infrastructure Security Agency) to provide guidance and support, and the development of new regulations aimed at critical infrastructure and federal contractors.
By 2026, we can expect to see further enhancements in these areas, with a stronger emphasis on information sharing, threat intelligence dissemination, and potentially more stringent cybersecurity mandates across various sectors. These governmental efforts provide a crucial framework and resources for organizations to improve their security posture against the cybersecurity threats 2026.
Public-Private Partnerships and Information Sharing
Effective defense against advanced cyber threats relies heavily on collaboration between the public and private sectors. Government agencies often possess unique threat intelligence and expertise, while private companies hold the innovation and operational capabilities. Sharing threat indicators, attack methodologies, and defensive strategies can create a collective defense mechanism that is more resilient than individual efforts.
Organizations like Information Sharing and Analysis Centers (ISACs) play a vital role in facilitating this exchange within specific industries. By actively participating in such partnerships, businesses can gain early warnings of emerging threats and learn best practices from their peers, significantly enhancing their ability to combat the cybersecurity threats 2026. Building trust and secure channels for this information exchange will be paramount.
International Cooperation
Cyber threats are inherently global, often originating from state-sponsored groups or criminal organizations operating across borders. Therefore, international cooperation is essential for attribution, prosecution, and the development of common cybersecurity standards. Diplomatic efforts, intelligence sharing with allied nations, and joint cyber defense exercises will become increasingly important in addressing the global dimension of cybersecurity threats 2026.
Working with international partners to disrupt cybercrime infrastructure, dismantle ransomware operations, and hold malicious actors accountable sends a strong deterrent message. This global collaboration ensures that no single nation or organization has to face these formidable challenges alone.
Conclusion: A Resilient Digital Future
The year 2026 will undoubtedly present a challenging cybersecurity landscape in the US, marked by sophisticated ransomware, AI-powered attacks, and pervasive supply chain vulnerabilities. These cybersecurity threats 2026 are not merely theoretical; they represent real and present dangers to our digital infrastructure, economic stability, and personal privacy.
However, by understanding these threats and implementing proactive, multi-layered defense strategies, individuals and organizations can significantly enhance their resilience. Embracing a zero-trust architecture, investing in advanced threat intelligence, continuously training human firewalls, and developing robust incident response plans are all critical components of a comprehensive security posture.
Furthermore, recognizing the indispensable role of government initiatives, public-private partnerships, and international cooperation will be key to building a collective defense. The future of our digital presence in the US hinges on our ability to adapt, innovate, and collaborate in the face of an ever-evolving adversary. By taking these steps, we can work towards a more secure and resilient digital future, capable of withstanding the most advanced cybersecurity threats 2026 has to offer.
The journey to enhanced cybersecurity is continuous, requiring vigilance, investment, and a commitment to perpetual improvement. Let this guide serve as a call to action, inspiring you to strengthen your defenses and contribute to a safer digital world for all.